COMMON WEAKNESS ENUMERATIONIncomplete

CWE-1321

Improperly Controlled Modification of Object Prototype Attributes ('Prototype Pollution')

The product receives input from an upstream component that specifies attributes that are to be initialized or updated in an object, but it does not properly control modifications of attributes of the object prototype.

Soyutlama

Variant

Yapı

Simple

Sömürü İhtimali

High

Problemi anla

Problem nedir?

The product receives input from an upstream component that specifies attributes that are to be initialized or updated in an object, but it does not properly control modifications of attributes of the object prototype.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Architecture and Design

Yaşam döngüsü evresi

Implementation

This weakness is often found in code that assigns object attributes based on user input, or merges or clones objects recursively.

Risk

Başarılı sömürü neye yol açar?

Read Application DataModify Application Data

Etkilenen güvenlik alanları: Confidentiality, Integrity, Availability

This weakness is usually exploited by using a special attribute of objects called proto, constructor, or prototype. Such attributes give access to the object prototype. An attacker can inject attributes that are used in other components by adding or modifying attributes of an object prototype. This creates attributes that exist on every object, or replace critical attributes with malicious ones. This can be problematic if the product depends on existence or non-existence of certain attributes, or uses pre-defined attributes of the object prototype (such as hasOwnProperty, toString, or valueOf).
DoS: Crash, Exit, or Restart

Etkilenen güvenlik alanları: Availability

An attacker can override existing attributes with ones that have incompatible type, which may lead to a crash.

Savunma

Nasıl önlenir ve çözülür?

Implementation

Uygulama aşaması savunması

Detay
By freezing the object prototype first (for example, Object.freeze(Object.prototype)), modification of the prototype becomes impossible.

Etkinlik: High

While this can mitigate this weakness completely, other methods are recommended when possible, especially in components used by upstream software ("libraries").

Architecture and Design

Mimari ve tasarım yaklaşımı

Detay
By blocking modifications of attributes that resolve to object prototype, such as proto or prototype, this weakness can be mitigated.

Etkinlik: High

Implementation

Input Validation

Detay
When handling untrusted objects, validating using a schema can be used.

Etkinlik: Limited

Implementation

Uygulama aşaması savunması

Detay
By using an object without prototypes (via Object.create(null) ), adding object prototype attributes by accessing the prototype via the special attributes becomes impossible, mitigating this weakness.

Etkinlik: High

Implementation

Uygulama aşaması savunması

Detay
Map can be used instead of objects in most cases. If Map methods are used instead of object attributes, it is not possible to access the object prototype or modify it.

Etkinlik: Moderate

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
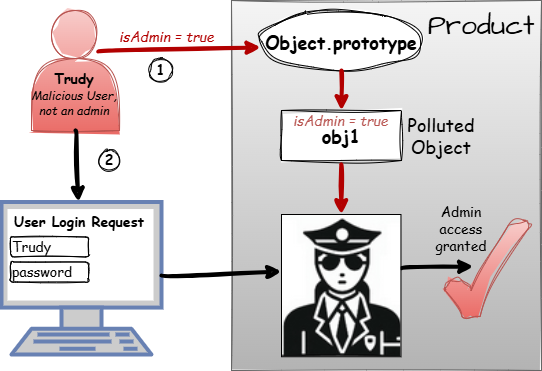
CWE-1321 MITRE diagramı