COMMON WEAKNESS ENUMERATIONDraft

CWE-184

Incomplete List of Disallowed Inputs

The product implements a protection mechanism that relies on a list of inputs (or properties of inputs) that are not allowed by policy or otherwise require other action to neutralize before additional processing takes place, but the list is incomplete.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The product implements a protection mechanism that relies on a list of inputs (or properties of inputs) that are not allowed by policy or otherwise require other action to neutralize before additional processing takes place, but the list is incomplete.

Terminoloji

Alternatif adlar ve kullanım biçimleri

Denylist / Deny List

This is used by CWE and CAPEC instead of other commonly-used terms. Its counterpart is allowlist.

Blocklist / Block List

This is often used by security tools such as firewalls, email or web gateways, proxies, etc.

Blacklist / Black List

This term is frequently used, but usage has been declining as organizations have started to adopt other terms.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Implementation

Developers often try to protect their products against malicious input by checking against lists of known bad inputs, such as special characters that can invoke new commands. However, such lists often only address the most well-known bad inputs. As a quick fix, developers might rely on these lists instead of addressing the root cause of the issue. See [REF-141].

Yaşam döngüsü evresi

Architecture and Design

The design might rely solely on detection of malicious inputs as a protection mechanism.

Risk

Başarılı sömürü neye yol açar?

Bypass Protection Mechanism

Etkilenen güvenlik alanları: Access Control

Attackers may be able to find other malicious inputs that were not expected by the developer, allowing them to bypass the intended protection mechanism.

Savunma

Nasıl önlenir ve çözülür?

Implementation

Input Validation

Detay
Do not rely exclusively on detecting disallowed inputs. There are too many variants to encode a character, especially when different environments are used, so there is a high likelihood of missing some variants. Only use detection of disallowed inputs as a mechanism for detecting suspicious activity. Ensure that you are using other protection mechanisms that only identify "good" input - such as lists of allowed inputs - and ensure that you are properly encoding your outputs.

Doğrulama

Nasıl tespit edilir?

Black Box

Exploitation of a vulnerability with commonly-used manipulations might fail, but minor variations might succeed.

MITRE görseli

Zafiyet ilişkisi ve akışı
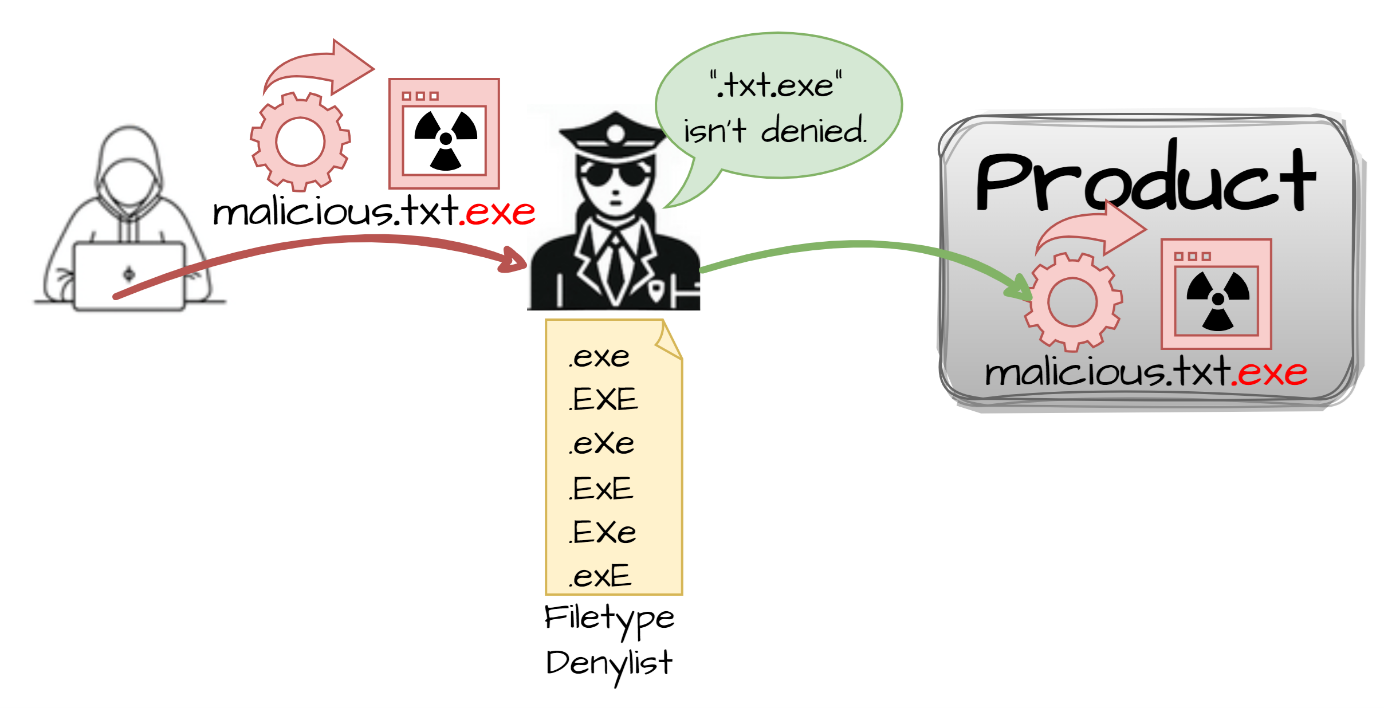
CWE-184 MITRE diagramı