COMMON WEAKNESS ENUMERATIONDraft

CWE-201

Insertion of Sensitive Information Into Sent Data

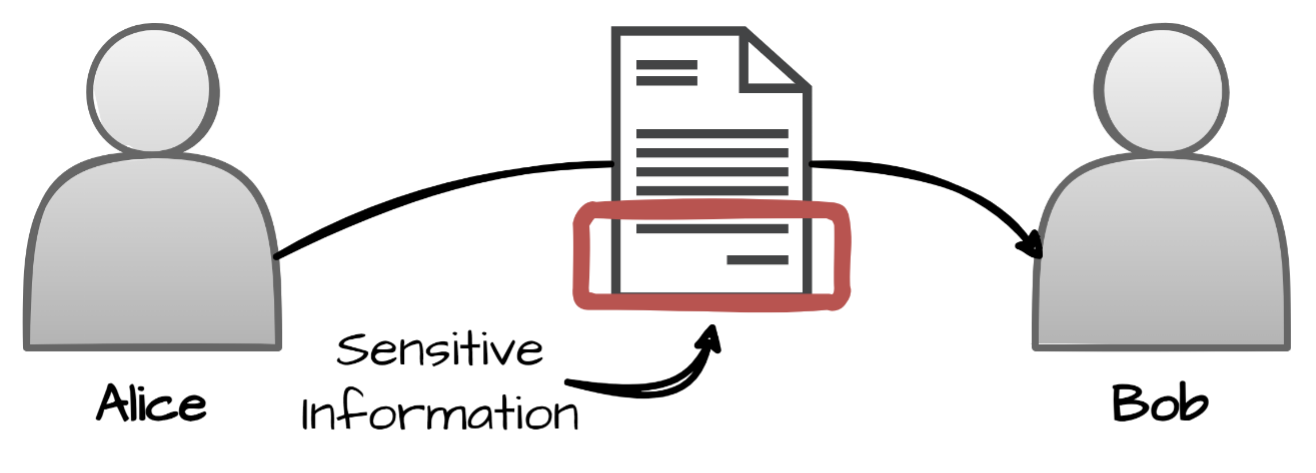
The code transmits data to another actor, but a portion of the data includes sensitive information that should not be accessible to that actor.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The code transmits data to another actor, but a portion of the data includes sensitive information that should not be accessible to that actor.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Architecture and Design

Yaşam döngüsü evresi

Implementation

REALIZATION: This weakness is caused during implementation of an architectural security tactic.

Risk

Başarılı sömürü neye yol açar?

Read Files or DirectoriesRead MemoryRead Application Data

Etkilenen güvenlik alanları: Confidentiality

Sensitive data may be exposed to attackers.

Savunma

Nasıl önlenir ve çözülür?

Requirements

Güvenlik gereksinimi

Detay
Specify which data in the software should be regarded as sensitive. Consider which types of users should have access to which types of data.

Implementation

Uygulama aşaması savunması

Detay
Ensure that any possibly sensitive data specified in the requirements is verified with designers to ensure that it is either a calculated risk or mitigated elsewhere. Any information that is not necessary to the functionality should be removed in order to lower both the overhead and the possibility of security sensitive data being sent.

System Configuration

Güvenli yapılandırma yaklaşımı

Detay
Setup default error messages so that unexpected errors do not disclose sensitive information.

Architecture and Design

Separation of Privilege

Detay
Compartmentalize the system to have "safe" areas where trust boundaries can be unambiguously drawn. Do not allow sensitive data to go outside of the trust boundary and always be careful when interfacing with a compartment outside of the safe area. Ensure that appropriate compartmentalization is built into the system design, and the compartmentalization allows for and reinforces privilege separation functionality. Architects and designers should rely on the principle of least privilege to decide the appropriate time to use privileges and the time to drop privileges.

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
CWE-201 MITRE diagramı