COMMON WEAKNESS ENUMERATIONIncomplete

CWE-256

Plaintext Storage of a Password

The product stores a password in plaintext within resources such as memory or files.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

High

Problemi anla

Problem nedir?

The product stores a password in plaintext within resources such as memory or files.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Architecture and Design

OMISSION: This weakness is caused by missing a security tactic during the architecture and design phase.

Yaşam döngüsü evresi

Architecture and Design

Developers sometimes believe that they cannot defend the application from someone who has access to the configuration, but this belief makes an attacker's job easier.

Risk

Başarılı sömürü neye yol açar?

Gain Privileges or Assume Identity

Etkilenen güvenlik alanları: Access Control

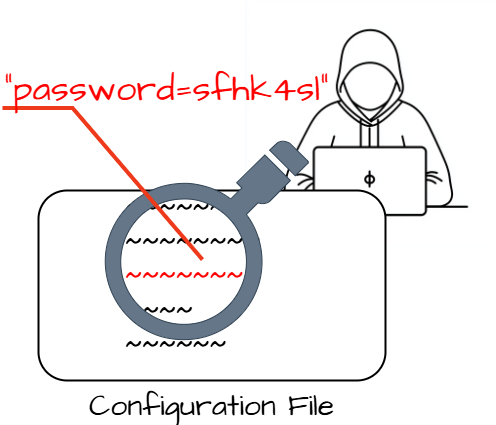
Storing a plaintext password in a configuration file allows anyone who can read the file to access the password-protected resource. In some contexts, even storage of a plaintext password in memory is considered a security risk if the password is not cleared immediately after it is used.

Savunma

Nasıl önlenir ve çözülür?

Architecture and Design

Mimari ve tasarım yaklaşımı

Detay
Avoid storing passwords in easily accessible locations.

Architecture and Design

Mimari ve tasarım yaklaşımı

Detay
Consider storing cryptographic hashes of passwords as an alternative to storing in plaintext.

Tüm evreler

Genel azaltım ve savunma yaklaşımı

Detay
A programmer might attempt to remedy the password management problem by obscuring the password with an encoding function, such as base 64 encoding, but this effort does not adequately protect the password because the encoding can be detected and decoded easily.

Etkinlik: None

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
CWE-256 MITRE diagramı