COMMON WEAKNESS ENUMERATIONDraft

CWE-276

Incorrect Default Permissions

During installation, installed file permissions are set to allow anyone to modify those files.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

During installation, installed file permissions are set to allow anyone to modify those files.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Architecture and Design

Yaşam döngüsü evresi

Implementation

Yaşam döngüsü evresi

Installation

Yaşam döngüsü evresi

Operation

Risk

Başarılı sömürü neye yol açar?

Read Application DataModify Application Data

Etkilenen güvenlik alanları: Confidentiality, Integrity

Savunma

Nasıl önlenir ve çözülür?

Architecture and Design · Operation

Birden fazla yaşam döngüsü evresinde uygulanacak savunma

Detay
The architecture needs to access and modification attributes for files to only those users who actually require those actions.

Architecture and Design

Separation of Privilege

Detay
Compartmentalize the system to have "safe" areas where trust boundaries can be unambiguously drawn. Do not allow sensitive data to go outside of the trust boundary and always be careful when interfacing with a compartment outside of the safe area. Ensure that appropriate compartmentalization is built into the system design, and the compartmentalization allows for and reinforces privilege separation functionality. Architects and designers should rely on the principle of least privilege to decide the appropriate time to use privileges and the time to drop privileges.

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis - Binary or Bytecode

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Inter-application Flow Analysis

Manual Static Analysis - Binary or Bytecode

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Binary / Bytecode disassembler - then use manual analysis for vulnerabilities & anomalies

Dynamic Analysis with Automated Results Interpretation

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Host-based Vulnerability Scanners - Examine configuration for flaws, verifying that audit mechanisms work, ensure host configuration meets certain predefined criteria Web Application Scanner Web Services Scanner Database Scanners

Dynamic Analysis with Manual Results Interpretation

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Host Application Interface Scanner ``` Cost effective for partial coverage: ``` Fuzz Tester Framework-based Fuzzer Automated Monitored Execution Forced Path Execution

Manual Static Analysis - Source Code

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Manual Source Code Review (not inspections) ``` Cost effective for partial coverage: ``` Focused Manual Spotcheck - Focused manual analysis of source

Automated Static Analysis - Source Code

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Context-configured Source Code Weakness Analyzer

Automated Static Analysis

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Configuration Checker

Architecture or Design Review

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Formal Methods / Correct-By-Construction ``` Cost effective for partial coverage: ``` Inspection (IEEE 1028 standard) (can apply to requirements, design, source code, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
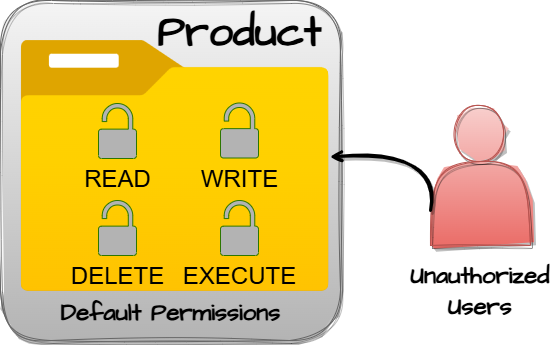
CWE-276 MITRE diagramı