COMMON WEAKNESS ENUMERATIONDraft

CWE-295

Improper Certificate Validation

The product does not validate, or incorrectly validates, a certificate.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The product does not validate, or incorrectly validates, a certificate.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Architecture and Design

Yaşam döngüsü evresi

Implementation

REALIZATION: This weakness is caused during implementation of an architectural security tactic.

Yaşam döngüsü evresi

Implementation

When the product uses certificate pinning, the developer might not properly validate all relevant components of the certificate before pinning the certificate. This can make it difficult or expensive to test after the pinning is complete.
A certificate is a token that associates an identity (principal) to a cryptographic key. Certificates can be used to check if a public key belongs to the assumed owner.

Risk

Başarılı sömürü neye yol açar?

Bypass Protection MechanismGain Privileges or Assume Identity

Etkilenen güvenlik alanları: Integrity, Authentication

When a certificate is invalid or malicious, it might allow an attacker to spoof a trusted entity by interfering in the communication path between the host and client. The product might connect to a malicious host while believing it is a trusted host, or the product might be deceived into accepting spoofed data that appears to originate from a trusted host.

Savunma

Nasıl önlenir ve çözülür?

Architecture and Design · Implementation

Birden fazla yaşam döngüsü evresinde uygulanacak savunma

Detay
Certificates should be carefully managed and checked to assure that data are encrypted with the intended owner's public key.

Implementation

Uygulama aşaması savunması

Detay
If certificate pinning is being used, ensure that all relevant properties of the certificate are fully validated before the certificate is pinned, including the hostname.

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis - Binary or Bytecode

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Bytecode Weakness Analysis - including disassembler + source code weakness analysis Binary Weakness Analysis - including disassembler + source code weakness analysis

Manual Static Analysis - Binary or Bytecode

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Binary / Bytecode disassembler - then use manual analysis for vulnerabilities & anomalies

Dynamic Analysis with Automated Results Interpretation

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Web Application Scanner

Dynamic Analysis with Manual Results Interpretation

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Man-in-the-middle attack tool

Manual Static Analysis - Source Code

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Focused Manual Spotcheck - Focused manual analysis of source Manual Source Code Review (not inspections)

Automated Static Analysis - Source Code

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Source code Weakness Analyzer Context-configured Source Code Weakness Analyzer

Architecture or Design Review

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Inspection (IEEE 1028 standard) (can apply to requirements, design, source code, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
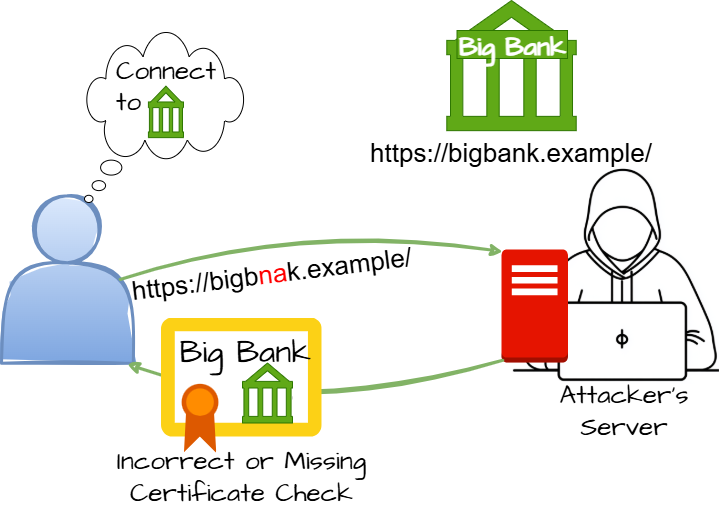
CWE-295 MITRE diagramı