COMMON WEAKNESS ENUMERATIONDraft

CWE-307

Improper Restriction of Excessive Authentication Attempts

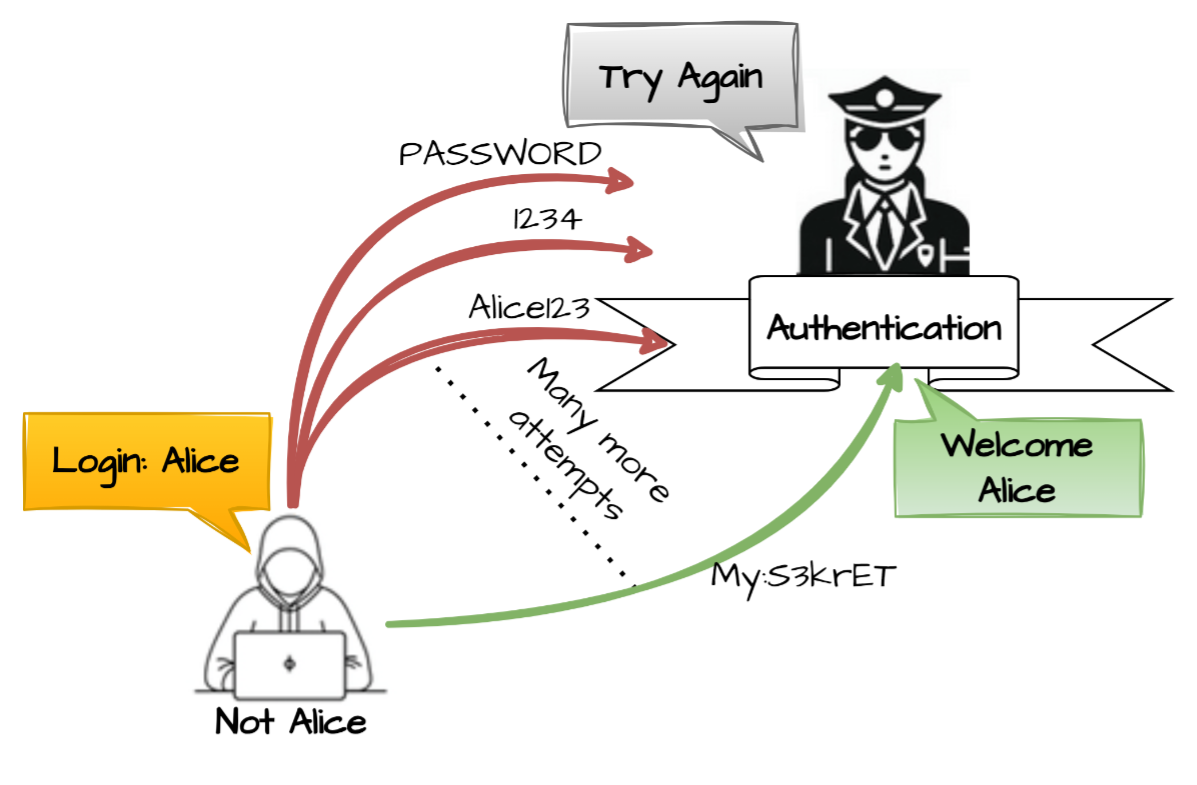
The product does not implement sufficient measures to prevent multiple failed authentication attempts within a short time frame.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The product does not implement sufficient measures to prevent multiple failed authentication attempts within a short time frame.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Architecture and Design

COMMISSION: This weakness refers to an incorrect design related to an architectural security tactic.

Risk

Başarılı sömürü neye yol açar?

Bypass Protection Mechanism

Etkilenen güvenlik alanları: Access Control

An attacker could perform an arbitrary number of authentication attempts using different passwords, and eventually gain access to the targeted account using a brute force attack.

Savunma

Nasıl önlenir ve çözülür?

Architecture and Design

Mimari ve tasarım yaklaşımı

Detay
Common protection mechanisms include: - Disconnecting the user after a small number of failed attempts - Implementing a timeout - Locking out a targeted account - Requiring a computational task on the user's part.

Architecture and Design

Libraries or Frameworks

Detay
Use a vetted library or framework that does not allow this weakness to occur or provides constructs that make this weakness easier to avoid [REF-1482]. Consider using libraries with authentication capabilities such as OpenSSL or the ESAPI Authenticator. [REF-45]

Doğrulama

Nasıl tespit edilir?

Dynamic Analysis with Automated Results Interpretation

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Web Application Scanner Web Services Scanner Database Scanners ``` Cost effective for partial coverage: ``` Host-based Vulnerability Scanners - Examine configuration for flaws, verifying that audit mechanisms work, ensure host configuration meets certain predefined criteria

Dynamic Analysis with Manual Results Interpretation

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Fuzz Tester Framework-based Fuzzer ``` Cost effective for partial coverage: ``` Forced Path Execution

Manual Static Analysis - Source Code

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Focused Manual Spotcheck - Focused manual analysis of source Manual Source Code Review (not inspections)

Automated Static Analysis - Source Code

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Source code Weakness Analyzer Context-configured Source Code Weakness Analyzer

Automated Static Analysis

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Configuration Checker

Architecture or Design Review

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Formal Methods / Correct-By-Construction ``` Cost effective for partial coverage: ``` Inspection (IEEE 1028 standard) (can apply to requirements, design, source code, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
CWE-307 MITRE diagramı
CWE-307: Common Weakness Enumeration Entry CWE-307 · DayBreach Sözlük · DayBreach