COMMON WEAKNESS ENUMERATIONStable

CWE-476

NULL Pointer Dereference

The product dereferences a pointer that it expects to be valid but is NULL.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The product dereferences a pointer that it expects to be valid but is NULL.

Terminoloji

Alternatif adlar ve kullanım biçimleri

NPD

Common abbreviation for Null Pointer Dereference

null deref

Common abbreviation for Null Pointer Dereference

NPE

Common abbreviation for Null Pointer Exception

nil pointer dereference

used for access of nil in Go programs

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Implementation

Risk

Başarılı sömürü neye yol açar?

DoS: Crash, Exit, or Restart

Etkilenen güvenlik alanları: Availability

NULL pointer dereferences usually result in the failure of the process unless exception handling (on some platforms) is available and implemented. Even when exception handling is being used, it can still be very difficult to return the software to a safe state of operation.
Execute Unauthorized Code or CommandsRead MemoryModify Memory

Etkilenen güvenlik alanları: Integrity, Confidentiality

In rare circumstances, when NULL is equivalent to the 0x0 memory address and privileged code can access it, then writing or reading memory is possible, which may lead to code execution.

Savunma

Nasıl önlenir ve çözülür?

Implementation

Uygulama aşaması savunması

Detay
For any pointers that could have been modified or provided from a function that can return NULL, check the pointer for NULL before use. When working with a multithreaded or otherwise asynchronous environment, ensure that proper locking APIs are used to lock before the check, and unlock when it has finished [REF-1484].

Requirements

Güvenlik gereksinimi

Detay
Select a programming language that is not susceptible to these issues.

Implementation

Uygulama aşaması savunması

Detay
Check the results of all functions that return a value and verify that the value is non-null before acting upon it.

Etkinlik: Moderate

Checking the return value of the function will typically be sufficient, however beware of race conditions (CWE-362) in a concurrent environment. This solution does not handle the use of improperly initialized variables (CWE-665).

Architecture and Design

Mimari ve tasarım yaklaşımı

Detay
Identify all variables and data stores that receive information from external sources, and apply input validation to make sure that they are only initialized to expected values.

Implementation

Uygulama aşaması savunması

Detay
Explicitly initialize all variables and other data stores, either during declaration or just before the first usage.

Doğrulama

Nasıl tespit edilir?

Automated Dynamic Analysis

Moderate
This weakness can be detected using dynamic tools and techniques that interact with the software using large test suites with many diverse inputs, such as fuzz testing (fuzzing), robustness testing, and fault injection. The software's operation may slow down, but it should not become unstable, crash, or generate incorrect results.

Manual Dynamic Analysis

Identify error conditions that are not likely to occur during normal usage and trigger them. For example, run the program under low memory conditions, run with insufficient privileges or permissions, interrupt a transaction before it is completed, or disable connectivity to basic network services such as DNS. Monitor the software for any unexpected behavior. If you trigger an unhandled exception or similar error that was discovered and handled by the application's environment, it may still indicate unexpected conditions that were not handled by the application itself.

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

Automated Dynamic Analysis

Moderate
Use tools that are integrated during compilation to insert runtime error-checking mechanisms related to memory safety errors, such as AddressSanitizer (ASan) for C/C++ [REF-1518].

Crafted inputs are necessary to reach the code containing the error, such as generated by fuzzers. Also, these tools may reduce performance, and they only report the error condition - not the original mistake that led to the error.

MITRE görseli

Zafiyet ilişkisi ve akışı
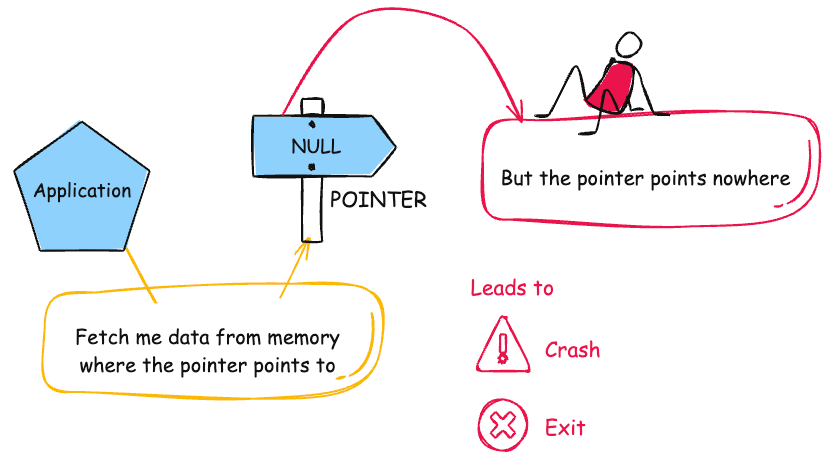
CWE-476 MITRE diagramı
CWE-476: NULL Pointer Dereference · DayBreach Sözlük · DayBreach