COMMON WEAKNESS ENUMERATIONDraft

CWE-489

Active Debug Code

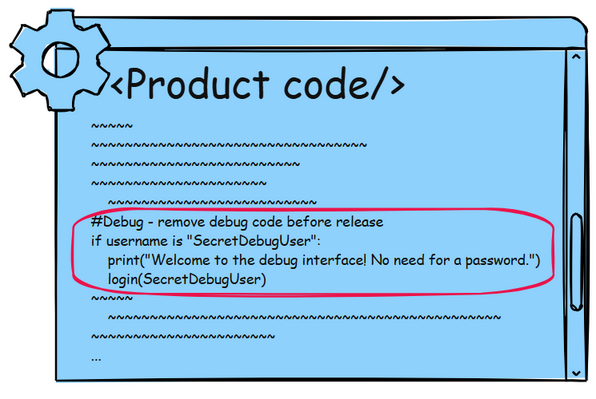
The product is released with debugging code still enabled or active.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The product is released with debugging code still enabled or active.

Terminoloji

Alternatif adlar ve kullanım biçimleri

Leftover debug code

This term originates from Seven Pernicious Kingdoms

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Implementation

In web-based applications, debug code is used to test and modify web application properties, configuration information, and functions. If a debug application is left on a production server, this oversight during the "software process" allows attackers access to debug functionality.

Yaşam döngüsü evresi

Implementation

A common development practice is to add "back door" code specifically designed for debugging or testing purposes that is not intended to be shipped or deployed with the product. These back door entry points create security risks because they are not considered during design or testing and fall outside of the expected operating conditions of the product.

Yaşam döngüsü evresi

Build and Compilation

Yaşam döngüsü evresi

Operation

Risk

Başarılı sömürü neye yol açar?

Bypass Protection MechanismRead Application DataGain Privileges or Assume IdentityVaries by Context

Etkilenen güvenlik alanları: Confidentiality, Integrity, Availability, Access Control, Other

Active debug code can create unintended entry points or expose sensitive information. The severity of the exposed debug code will depend on the particular instance. At the least, it will give an attacker sensitive information about the settings and mechanics of web applications on the server. At worst, as is often the case, the debug code will allow an attacker complete control over the web application and server, as well as confidential information that either of these access.

Savunma

Nasıl önlenir ve çözülür?

Build and Compilation · Distribution

Birden fazla yaşam döngüsü evresinde uygulanacak savunma

Detay
Remove debug code before deploying the application.

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
CWE-489 MITRE diagramı