COMMON WEAKNESS ENUMERATIONDraft

CWE-502

Deserialization of Untrusted Data

The product deserializes untrusted data without sufficiently ensuring that the resulting data will be valid.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The product deserializes untrusted data without sufficiently ensuring that the resulting data will be valid.

Terminoloji

Alternatif adlar ve kullanım biçimleri

Marshaling/Marshalling, Unmarshaling/Unmarshalling

Marshaling and unmarshaling are effectively synonyms for serialization and deserialization, respectively.

Pickling, Unpickling

In Python, the "pickle" functionality is used to perform serialization and deserialization.

PHP Object Injection

Some PHP application researchers use this term when attacking unsafe use of the unserialize() function; but it is also used for CWE-915.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Architecture and Design

OMISSION: This weakness is caused by missing a security tactic during the architecture and design phase.

Yaşam döngüsü evresi

Implementation

Serialization and deserialization refer to the process of taking program-internal object-related data, packaging it in a way that allows the data to be externally stored or transferred ("serialization"), then extracting the serialized data to reconstruct the original object ("deserialization").

Risk

Başarılı sömürü neye yol açar?

Modify Application DataUnexpected State

Etkilenen güvenlik alanları: Integrity

Attackers can modify unexpected objects or data that was assumed to be safe from modification. Deserialized data or code could be modified without using the provided accessor functions, or unexpected functions could be invoked.
DoS: Resource Consumption (CPU)

Etkilenen güvenlik alanları: Availability

If a function is making an assumption on when to terminate, based on a sentry in a string, it could easily never terminate.
Varies by Context

Etkilenen güvenlik alanları: Other

The consequences can vary widely, because it depends on which objects or methods are being deserialized, and how they are used. Making an assumption that the code in the deserialized object is valid is dangerous and can enable exploitation. One example is attackers using gadget chains to perform unauthorized actions, such as generating a shell.

Savunma

Nasıl önlenir ve çözülür?

Architecture and Design · Implementation

Birden fazla yaşam döngüsü evresinde uygulanacak savunma

Detay
If available, use the signing/sealing features of the programming language to assure that deserialized data has not been tainted. For example, a hash-based message authentication code (HMAC) could be used to ensure that data has not been modified.

Implementation

Uygulama aşaması savunması

Detay
When deserializing data, populate a new object rather than just deserializing. The result is that the data flows through safe input validation and that the functions are safe.

Implementation

Uygulama aşaması savunması

Detay
Explicitly define a final object() to prevent deserialization.

Architecture and Design · Implementation

Birden fazla yaşam döngüsü evresinde uygulanacak savunma

Detay
Make fields transient to protect them from deserialization. An attempt to serialize and then deserialize a class containing transient fields will result in NULLs where the transient data should be. This is an excellent way to prevent time, environment-based, or sensitive variables from being carried over and used improperly.

Implementation

Uygulama aşaması savunması

Detay
Avoid having unnecessary types or gadgets (a sequence of instances and method invocations that can self-execute during the deserialization process, often found in libraries) available that can be leveraged for malicious ends. This limits the potential for unintended or unauthorized types and gadgets to be leveraged by the attacker. Add only acceptable classes to an allowlist. Note: new gadgets are constantly being discovered, so this alone is not a sufficient mitigation.

Architecture and Design · Implementation

Birden fazla yaşam döngüsü evresinde uygulanacak savunma

Detay
Employ cryptography of the data or code for protection. However, it's important to note that it would still be client-side security. This is risky because if the client is compromised then the security implemented on the client (the cryptography) can be bypassed.

Operation

Firewall

Detay
Use an application firewall that can detect attacks against this weakness. It can be beneficial in cases in which the code cannot be fixed (because it is controlled by a third party), as an emergency prevention measure while more comprehensive software assurance measures are applied, or to provide defense in depth [REF-1481].

Etkinlik: Moderate

An application firewall might not cover all possible input vectors. In addition, attack techniques might be available to bypass the protection mechanism, such as using malformed inputs that can still be processed by the component that receives those inputs. Depending on functionality, an application firewall might inadvertently reject or modify legitimate requests. Finally, some manual effort may be required for customization.

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
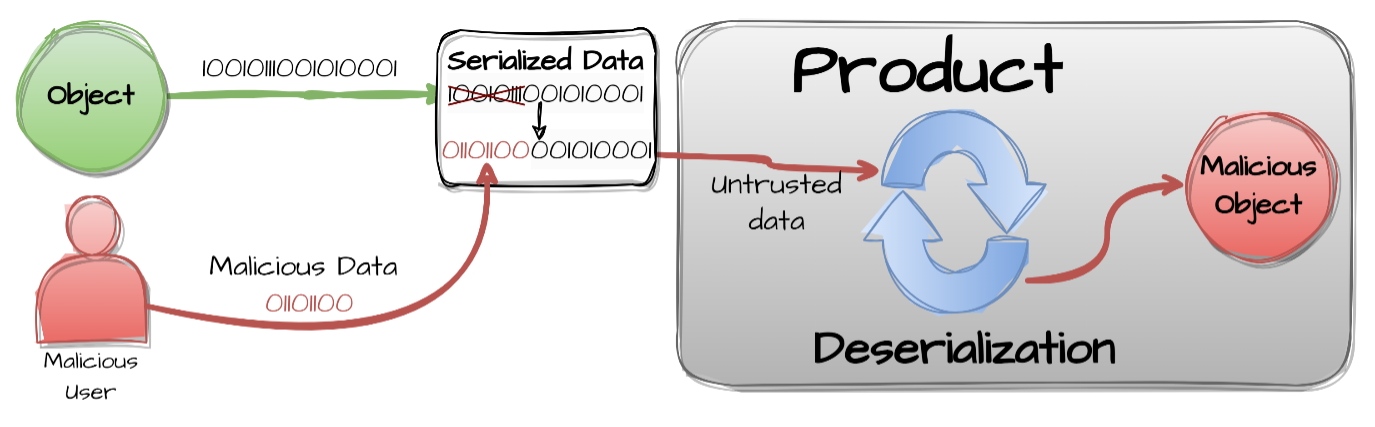
CWE-502 MITRE diagramı