COMMON WEAKNESS ENUMERATIONIncomplete

CWE-565

Reliance on Cookies without Validation and Integrity Checking

The product relies on the existence or values of cookies when performing security-critical operations, but it does not properly ensure that the setting is valid for the associated user.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The product relies on the existence or values of cookies when performing security-critical operations, but it does not properly ensure that the setting is valid for the associated user.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Architecture and Design

OMISSION: This weakness is caused by missing a security tactic during the architecture and design phase.

Yaşam döngüsü evresi

Implementation

Risk

Başarılı sömürü neye yol açar?

Modify Application DataExecute Unauthorized Code or Commands

Etkilenen güvenlik alanları: Confidentiality, Integrity, Availability

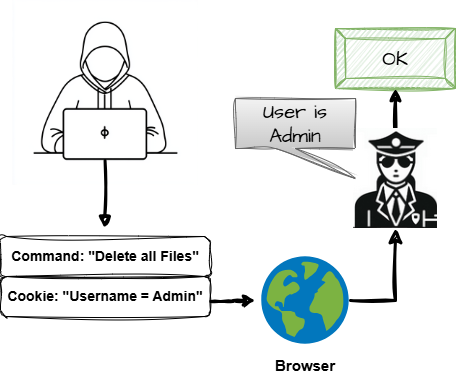
Attackers can easily modify cookies, within the browser or by implementing the client-side code outside of the browser. Reliance on cookies without detailed validation and integrity checking can allow attackers to bypass authentication, conduct injection attacks such as SQL injection and cross-site scripting, or otherwise modify inputs in unexpected ways.
Gain Privileges or Assume Identity

Etkilenen güvenlik alanları: Access Control

It is dangerous to use cookies to set a user's privileges. The cookie can be manipulated to escalate an attacker's privileges to an administrative level.

Savunma

Nasıl önlenir ve çözülür?

Architecture and Design

Mimari ve tasarım yaklaşımı

Detay
Avoid using cookie data for a security-related decision.

Implementation

Uygulama aşaması savunması

Detay
Perform thorough input validation (i.e.: server side validation) on the cookie data if you're going to use it for a security related decision.

Architecture and Design

Mimari ve tasarım yaklaşımı

Detay
Add integrity checks to detect tampering.

Architecture and Design

Mimari ve tasarım yaklaşımı

Detay
Protect critical cookies from replay attacks, since cross-site scripting or other attacks may allow attackers to steal a strongly-encrypted cookie that also passes integrity checks. This mitigation applies to cookies that should only be valid during a single transaction or session. By enforcing timeouts, you may limit the scope of an attack. As part of your integrity check, use an unpredictable, server-side value that is not exposed to the client.

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
CWE-565 MITRE diagramı