COMMON WEAKNESS ENUMERATIONIncomplete

CWE-918

Server-Side Request Forgery (SSRF)

The web server receives a URL or similar request from an upstream component and retrieves the contents of this URL, but it does not sufficiently ensure that the request is being sent to the expected destination.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

High

Problemi anla

Problem nedir?

The web server receives a URL or similar request from an upstream component and retrieves the contents of this URL, but it does not sufficiently ensure that the request is being sent to the expected destination.

Terminoloji

Alternatif adlar ve kullanım biçimleri

XSPA

Cross Site Port Attack

SSRF

Server-Side Request Forgery

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Architecture and Design

Yaşam döngüsü evresi

Implementation

Risk

Başarılı sömürü neye yol açar?

Read Application Data

Etkilenen güvenlik alanları: Confidentiality

Execute Unauthorized Code or Commands

Etkilenen güvenlik alanları: Integrity

Bypass Protection Mechanism

Etkilenen güvenlik alanları: Access Control

By providing URLs to unexpected hosts or ports, attackers can make it appear that the server is sending the request, possibly bypassing access controls such as firewalls that prevent the attackers from accessing the URLs directly. The server can be used as a proxy to conduct port scanning of hosts in internal networks, use other URLs such as that can access documents on the system (using file://), or use other protocols such as gopher:// or tftp://, which may provide greater control over the contents of requests.

Savunma

Nasıl önlenir ve çözülür?

  • Maintain an allowlist of allowed domains/IPs
  • Block requests to local/loopback and metadata IP addresses (169.254.169.254)

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
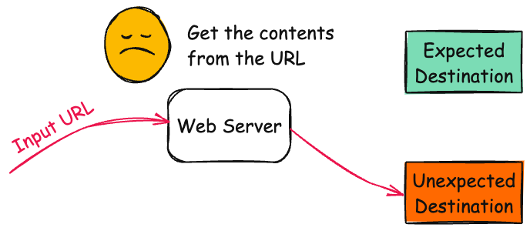
CWE-918 MITRE diagramı
CWE-918: Server-Side Request Forgery (SSRF) · DayBreach Sözlük · DayBreach