COMMON WEAKNESS ENUMERATIONDraft

CWE-93

Improper Neutralization of CRLF Sequences ('CRLF Injection')

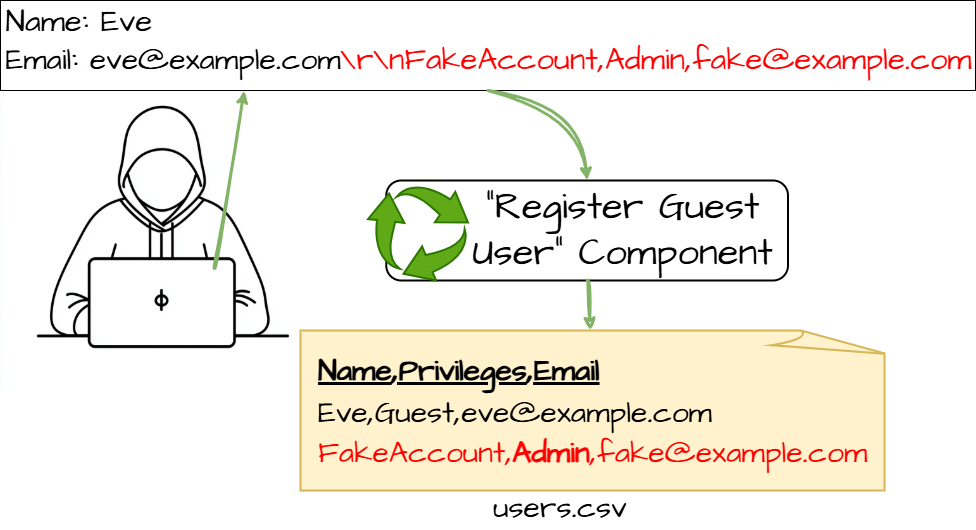
The product uses CRLF (carriage return line feeds) as a special element, e.g. to separate lines or records, but it does not neutralize or incorrectly neutralizes CRLF sequences from inputs.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The product uses CRLF (carriage return line feeds) as a special element, e.g. to separate lines or records, but it does not neutralize or incorrectly neutralizes CRLF sequences from inputs.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Implementation

REALIZATION: This weakness is caused during implementation of an architectural security tactic.

Risk

Başarılı sömürü neye yol açar?

Modify Application Data

Etkilenen güvenlik alanları: Integrity

Savunma

Nasıl önlenir ve çözülür?

Implementation

Uygulama aşaması savunması

Detay
Avoid using CRLF as a special sequence.

Implementation

Uygulama aşaması savunması

Detay
Appropriately filter or quote CRLF sequences in user-controlled input.

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
CWE-93 MITRE diagramı
CWE-93: Common Weakness Enumeration Entry CWE-93 · DayBreach Sözlük · DayBreach