COMMON WEAKNESS ENUMERATIONDraft

CWE-125

Out-of-bounds Read

The product reads data past the end, or before the beginning, of the intended buffer.

Abstraction

Base

Structure

Simple

Likelihood of Exploit

High

Understand the problem

What is the problem?

The product reads data past the end, or before the beginning, of the intended buffer.

Terminology

Alternate terms and usages

OOB read

Shorthand for "Out of bounds" read

Root cause

How and when does the problem arise?

Lifecycle phase

Implementation

Risk

What does successful exploitation lead to?

Read Memory

Affected security scopes: Confidentiality

An attacker could get secret values such as cryptographic keys, PII, memory addresses, or other information that could be used in additional attacks.
Bypass Protection Mechanism

Affected security scopes: Confidentiality

Out-of-bounds memory could contain memory addresses or other information that can be used to bypass ASLR and other protection mechanisms in order to improve the reliability of exploiting a separate weakness for code execution.
DoS: Crash, Exit, or Restart

Affected security scopes: Availability

An attacker could cause a segmentation fault or crash by causing memory to be read outside of the bounds of the buffer. This is especially likely when the code reads a variable amount of data and assumes that a sentinel exists to stop the read operation, such as a NUL in a string.
Varies by Context

Affected security scopes: Other

The read operation could produce other undefined or unexpected results.

Defence

How is it prevented and fixed?

Implementation

Input Validation

Detail
Assume all input is malicious. Use an "accept known good" input validation strategy, i.e., use a list of acceptable inputs that strictly conform to specifications. Reject any input that does not strictly conform to specifications, or transform it into something that does. When performing input validation, consider all potentially relevant properties, including length, type of input, the full range of acceptable values, missing or extra inputs, syntax, consistency across related fields, and conformance to business rules. As an example of business rule logic, "boat" may be syntactically valid because it only contains alphanumeric characters, but it is not valid if the input is only expected to contain colors such as "red" or "blue." Do not rely exclusively on looking for malicious or malformed inputs. This is likely to miss at least one undesirable input, especially if the code's environment changes. This can give attackers enough room to bypass the intended validation. However, denylists can be useful for detecting potential attacks or determining which inputs are so malformed that they should be rejected outright. To reduce the likelihood of introducing an out-of-bounds read, ensure that you validate and ensure correct calculations for any length argument, buffer size calculation, or offset. Be especially careful of relying on a sentinel (i.e. special character such as NUL) in untrusted inputs.

Architecture and Design

Language Selection

Detail
Use a language that provides appropriate memory abstractions.

Verification

How is it detected?

Fuzzing

High
Fuzz testing (fuzzing) is a powerful technique for generating large numbers of diverse inputs - either randomly or algorithmically - and dynamically invoking the code with those inputs. Even with random inputs, it is often capable of generating unexpected results such as crashes, memory corruption, or resource consumption. Fuzzing effectively produces repeatable test cases that clearly indicate bugs, which helps developers to diagnose the issues.

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

Automated Dynamic Analysis

Moderate
Use tools that are integrated during compilation to insert runtime error-checking mechanisms related to memory safety errors, such as AddressSanitizer (ASan) for C/C++ [REF-1518].

Crafted inputs are necessary to reach the code containing the error, such as generated by fuzzers. Also, these tools may reduce performance, and they only report the error condition - not the original mistake that led to the error.

MITRE diagram

Weakness relationships and flow
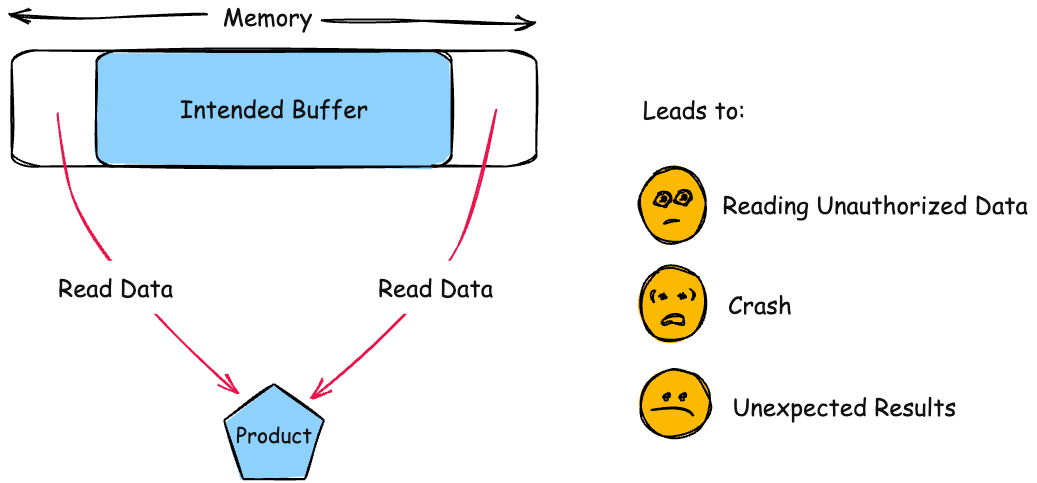
CWE-125 MITRE diagramı