COMMON WEAKNESS ENUMERATIONDraft

CWE-1333

Inefficient Regular Expression Complexity

The product uses a regular expression with a worst-case computational complexity that is inefficient and possibly exponential.

Abstraction

Base

Structure

Simple

Likelihood of Exploit

High

Understand the problem

What is the problem?

The product uses a regular expression with a worst-case computational complexity that is inefficient and possibly exponential.

Terminology

Alternate terms and usages

ReDoS

ReDoS is an abbreviation of "Regular expression Denial of Service".

Regular Expression Denial of Service

While this term is attack-focused, this is commonly used to describe the weakness.

Catastrophic backtracking

This term is used to describe the behavior of the regular expression as a negative technical impact.

Root cause

How and when does the problem arise?

Lifecycle phase

Implementation

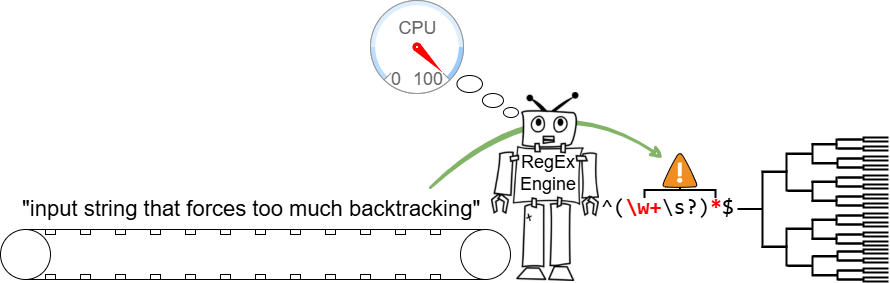
A RegEx can be easy to create and read using unbounded matching characters, but the programmer might not consider the risk of excessive backtracking.

Lifecycle phase

Implementation

Backtracking becomes a weakness if all of these conditions are met: - The number of possible backtracking attempts is exponential relative to the length of the input. - The input can fail to match the regular expression. - The input can be long enough.
Some regular expression engines have a feature called "backtracking". If the token cannot match, the engine "backtracks" to a position that may result in a different token that can match.

Risk

What does successful exploitation lead to?

DoS: Resource Consumption (CPU)

Affected security scopes: Availability

Attackers can create crafted inputs that intentionally cause the regular expression to use excessive backtracking in a way that causes the CPU consumption to spike.

Defence

How is it prevented and fixed?

Architecture and Design

Architecture and design approach

Detail
Use regular expressions that do not support backtracking, e.g. by removing nested quantifiers.

Effectiveness: High

This is one of the few effective solutions when using user-provided regular expressions.

System Configuration

Secure configuration approach

Detail
Set backtracking limits in the configuration of the regular expression implementation, such as PHP's pcre.backtrack_limit. Also consider limits on execution time for the process.

Effectiveness: Moderate

Implementation

Implementation-phase defence

Detail
Do not use regular expressions with untrusted input. If regular expressions must be used, avoid using backtracking in the expression.

Effectiveness: High

Implementation

Implementation-phase defence

Detail
Limit the length of the input that the regular expression will process.

Effectiveness: Moderate

Verification

How is it detected?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE diagram

Weakness relationships and flow
CWE-1333 MITRE diagramı