CWE-23
Relative Path Traversal
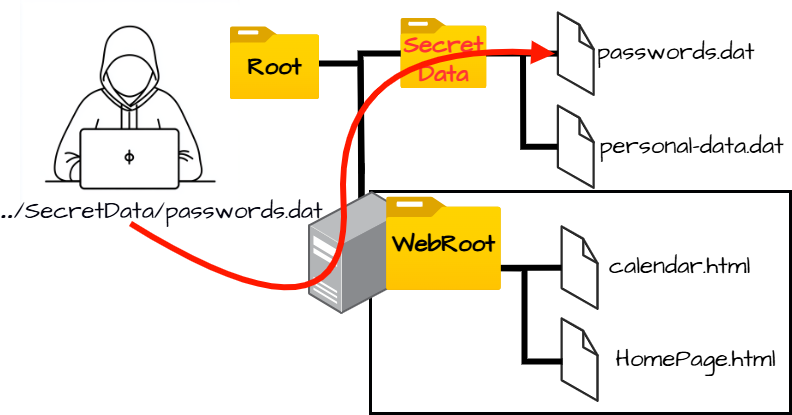
The product uses external input to construct a pathname that should be within a restricted directory, but it does not properly neutralize sequences such as ".." that can resolve to a location that is outside of that directory.
Abstraction
Base
Structure
Simple
Likelihood of Exploit
Medium
Understand the problem
What is the problem?
Terminology
Alternate terms and usages
Zip Slip
Root cause
How and when does the problem arise?
Lifecycle phase
Implementation
Risk
What does successful exploitation lead to?
Affected security scopes: Integrity, Confidentiality, Availability
Affected security scopes: Integrity
Affected security scopes: Confidentiality
Affected security scopes: Availability
Defence
How is it prevented and fixed?
Implementation
Input Validation
Detail
Implementation
Input Validation
Implementation
Input Validation
Detail
Implementation
Input Validation
Operation
Firewall
Detail
Operation
Firewall
Effectiveness: Moderate
An application firewall might not cover all possible input vectors. In addition, attack techniques might be available to bypass the protection mechanism, such as using malformed inputs that can still be processed by the component that receives those inputs. Depending on functionality, an application firewall might inadvertently reject or modify legitimate requests. Finally, some manual effort may be required for customization.
Verification
How is it detected?
Automated Static Analysis
HighMITRE diagram
Weakness relationships and flow