COMMON WEAKNESS ENUMERATIONDraft

CWE-269

Improper Privilege Management

The product does not properly assign, modify, track, or check privileges for an actor, creating an unintended sphere of control for that actor.

Abstraction

Class

Structure

Simple

Likelihood of Exploit

Medium

Understand the problem

What is the problem?

The product does not properly assign, modify, track, or check privileges for an actor, creating an unintended sphere of control for that actor.

Root cause

How and when does the problem arise?

Lifecycle phase

Architecture and Design

Lifecycle phase

Implementation

REALIZATION: This weakness is caused during implementation of an architectural security tactic.

Lifecycle phase

Operation

Risk

What does successful exploitation lead to?

Gain Privileges or Assume Identity

Affected security scopes: Access Control

Defence

How is it prevented and fixed?

Architecture and Design · Operation

Defence to apply across several lifecycle phases

Detail
Very carefully manage the setting, management, and handling of privileges. Explicitly manage trust zones in the software.

Architecture and Design

Separation of Privilege

Detail
Follow the principle of least privilege when assigning access rights to entities in a software system.

Architecture and Design

Separation of Privilege

Detail
Consider following the principle of separation of privilege. Require multiple conditions to be met before permitting access to a system resource.

Verification

How is it detected?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE diagram

Weakness relationships and flow
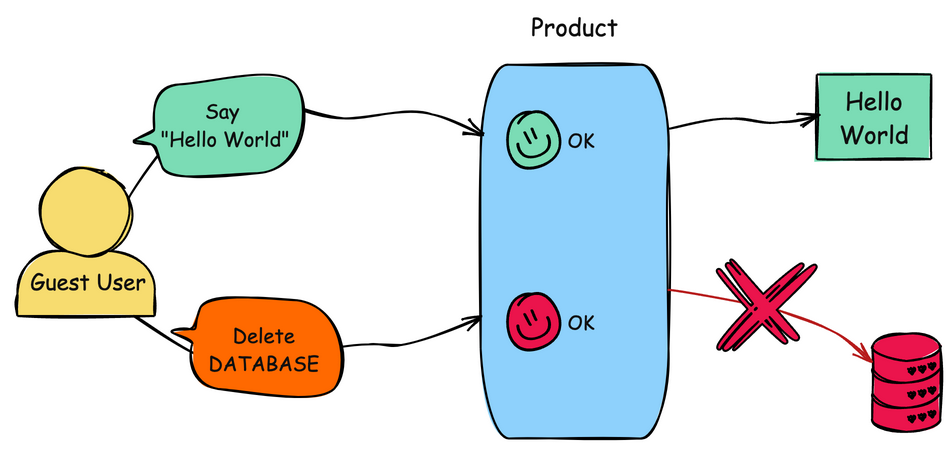
CWE-269 MITRE diagramı
CWE-269: Common Weakness Enumeration Entry CWE-269 · DayBreach Sözlük · DayBreach