COMMON WEAKNESS ENUMERATIONDraft

CWE-276

Incorrect Default Permissions

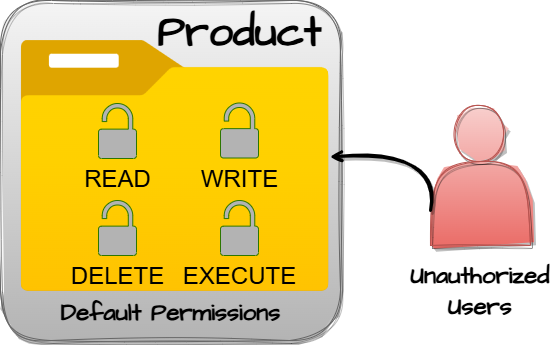
During installation, installed file permissions are set to allow anyone to modify those files.

Abstraction

Base

Structure

Simple

Likelihood of Exploit

Medium

Understand the problem

What is the problem?

During installation, installed file permissions are set to allow anyone to modify those files.

Root cause

How and when does the problem arise?

Lifecycle phase

Architecture and Design

Lifecycle phase

Implementation

Lifecycle phase

Installation

Lifecycle phase

Operation

Risk

What does successful exploitation lead to?

Read Application DataModify Application Data

Affected security scopes: Confidentiality, Integrity

Defence

How is it prevented and fixed?

Architecture and Design · Operation

Defence to apply across several lifecycle phases

Detail
The architecture needs to access and modification attributes for files to only those users who actually require those actions.

Architecture and Design

Separation of Privilege

Detail
Compartmentalize the system to have "safe" areas where trust boundaries can be unambiguously drawn. Do not allow sensitive data to go outside of the trust boundary and always be careful when interfacing with a compartment outside of the safe area. Ensure that appropriate compartmentalization is built into the system design, and the compartmentalization allows for and reinforces privilege separation functionality. Architects and designers should rely on the principle of least privilege to decide the appropriate time to use privileges and the time to drop privileges.

Verification

How is it detected?

Automated Static Analysis - Binary or Bytecode

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Inter-application Flow Analysis

Manual Static Analysis - Binary or Bytecode

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Binary / Bytecode disassembler - then use manual analysis for vulnerabilities & anomalies

Dynamic Analysis with Automated Results Interpretation

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Host-based Vulnerability Scanners - Examine configuration for flaws, verifying that audit mechanisms work, ensure host configuration meets certain predefined criteria Web Application Scanner Web Services Scanner Database Scanners

Dynamic Analysis with Manual Results Interpretation

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Host Application Interface Scanner ``` Cost effective for partial coverage: ``` Fuzz Tester Framework-based Fuzzer Automated Monitored Execution Forced Path Execution

Manual Static Analysis - Source Code

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Manual Source Code Review (not inspections) ``` Cost effective for partial coverage: ``` Focused Manual Spotcheck - Focused manual analysis of source

Automated Static Analysis - Source Code

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Context-configured Source Code Weakness Analyzer

Automated Static Analysis

SOAR Partial
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Cost effective for partial coverage: ``` Configuration Checker

Architecture or Design Review

High
According to SOAR [REF-1479], the following detection techniques may be useful: ``` Highly cost effective: ``` Formal Methods / Correct-By-Construction ``` Cost effective for partial coverage: ``` Inspection (IEEE 1028 standard) (can apply to requirements, design, source code, etc.)

MITRE diagram

Weakness relationships and flow
CWE-276 MITRE diagramı