COMMON WEAKNESS ENUMERATIONIncomplete

CWE-288

Authentication Bypass Using an Alternate Path or Channel

The product requires authentication, but the product has an alternate path or channel that does not require authentication.

Abstraction

Base

Structure

Simple

Likelihood of Exploit

Medium

Understand the problem

What is the problem?

The product requires authentication, but the product has an alternate path or channel that does not require authentication.

Root cause

How and when does the problem arise?

Lifecycle phase

Architecture and Design

COMMISSION: This weakness refers to an incorrect design related to an architectural security tactic.

Lifecycle phase

Architecture and Design

This is often seen in web applications that assume that access to a particular CGI program can only be obtained through a "front" screen, when the supporting programs are directly accessible. But this problem is not just in web apps.

Risk

What does successful exploitation lead to?

Bypass Protection Mechanism

Affected security scopes: Access Control

Defence

How is it prevented and fixed?

Architecture and Design

Architecture and design approach

Detail
Funnel all access through a single choke point to simplify how users can access a resource. For every access, perform a check to determine if the user has permissions to access the resource.

MITRE diagram

Weakness relationships and flow
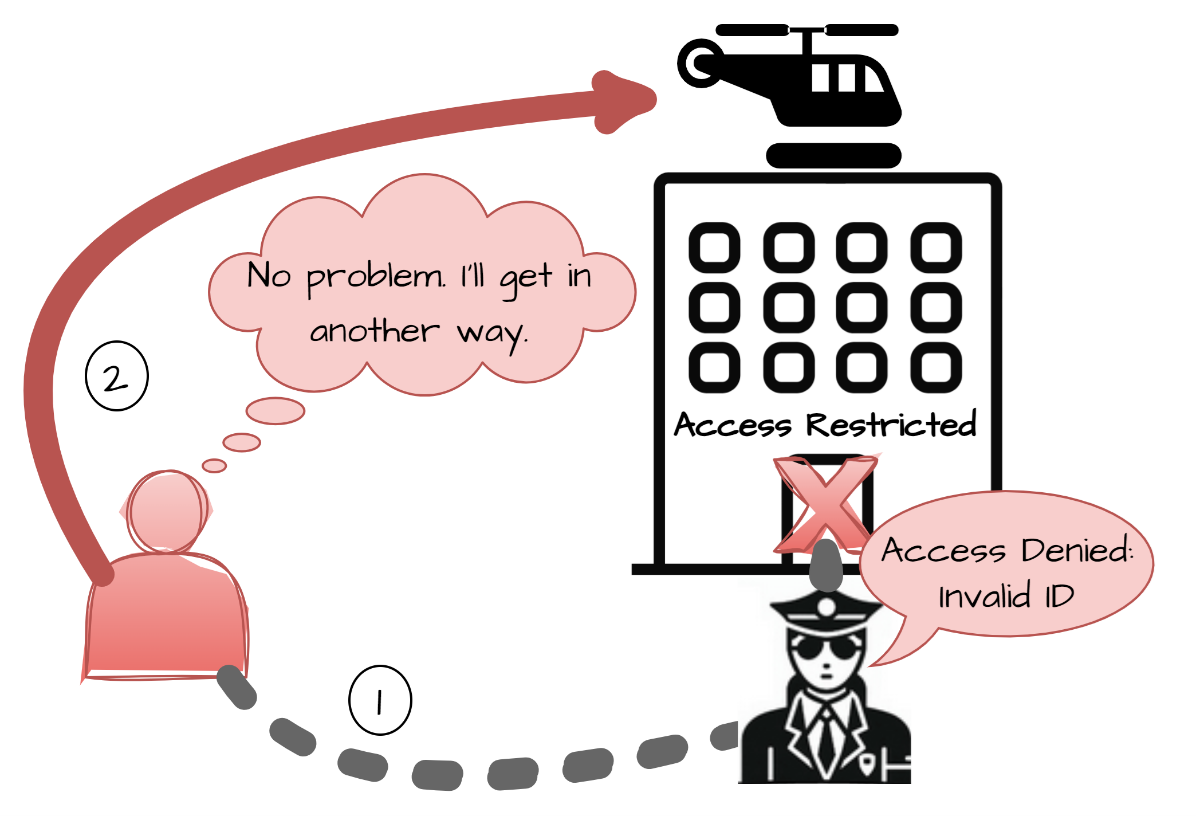
CWE-288 MITRE diagramı