COMMON WEAKNESS ENUMERATIONDraft

CWE-298

Improper Validation of Certificate Expiration

A certificate expiration is not validated or is incorrectly validated.

Abstraction

Variant

Structure

Simple

Likelihood of Exploit

Low

Understand the problem

What is the problem?

A certificate expiration is not validated or is incorrectly validated.

Root cause

How and when does the problem arise?

Lifecycle phase

Implementation

When the software uses certificate pinning, the developer might not properly validate all relevant components of the certificate before pinning the certificate. This can make it difficult or expensive to test after the pinning is complete.

Lifecycle phase

Implementation

REALIZATION: This weakness is caused during implementation of an architectural security tactic.

Risk

What does successful exploitation lead to?

Other

Affected security scopes: Integrity, Other

The data read from the system vouched for by the expired certificate may be flawed due to malicious spoofing.
Other

Affected security scopes: Authentication, Other

Trust may be assigned to certificates that have been abandoned due to age.

Defence

How is it prevented and fixed?

Architecture and Design

Architecture and design approach

Detail
Check for expired certificates and provide the user with adequate information about the nature of the problem and how to proceed.

Implementation

Implementation-phase defence

Detail
If certificate pinning is being used, ensure that all relevant properties of the certificate are fully validated before the certificate is pinned, including the expiration.

MITRE diagram

Weakness relationships and flow
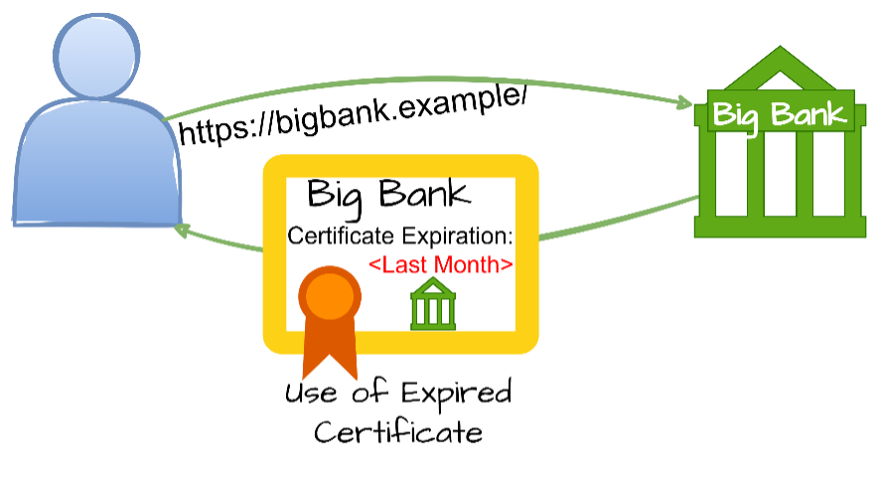
CWE-298 MITRE diagramı