COMMON WEAKNESS ENUMERATIONDraft
CWE-502
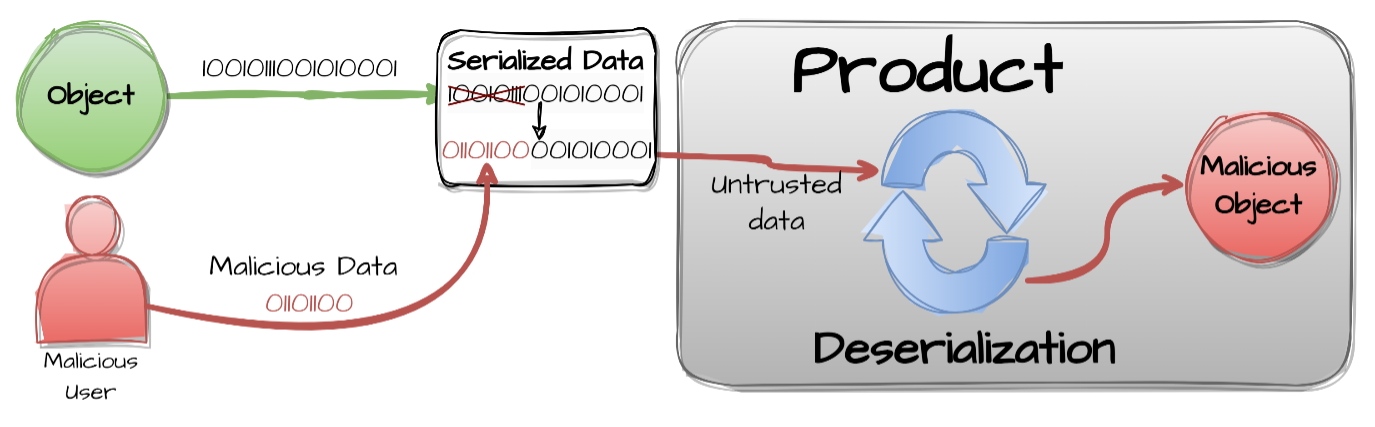
Deserialization of Untrusted Data
Abstraction
Base
Structure
Simple
Likelihood of Exploit
Medium
Understand the problem
What is the problem?
Terminology
Alternate terms and usages
Marshaling/Marshalling, Unmarshaling/Unmarshalling
Pickling, Unpickling
PHP Object Injection
Root cause
How and when does the problem arise?
Lifecycle phase
Architecture and Design
Lifecycle phase
Implementation
Risk
What does successful exploitation lead to?
Modify Application DataUnexpected State
DoS: Resource Consumption (CPU)
Varies by Context
Defence
How is it prevented and fixed?
Architecture and Design · Implementation
Defence to apply across several lifecycle phases
Detail
Architecture and Design · Implementation
Defence to apply across several lifecycle phases
Implementation
Implementation-phase defence
Detail
Implementation
Implementation-phase defence
Implementation
Implementation-phase defence
Detail
Implementation
Implementation-phase defence
Architecture and Design · Implementation
Defence to apply across several lifecycle phases
Detail
Architecture and Design · Implementation
Defence to apply across several lifecycle phases
Implementation
Implementation-phase defence
Detail
Implementation
Implementation-phase defence
Architecture and Design · Implementation
Defence to apply across several lifecycle phases
Detail
Architecture and Design · Implementation
Defence to apply across several lifecycle phases
Operation
Firewall
Detail
Operation
Firewall
Verification
How is it detected?
Automated Static Analysis
HighMITRE diagram
Weakness relationships and flow