COMMON WEAKNESS ENUMERATIONIncomplete

CWE-532

Insertion of Sensitive Information into Log File

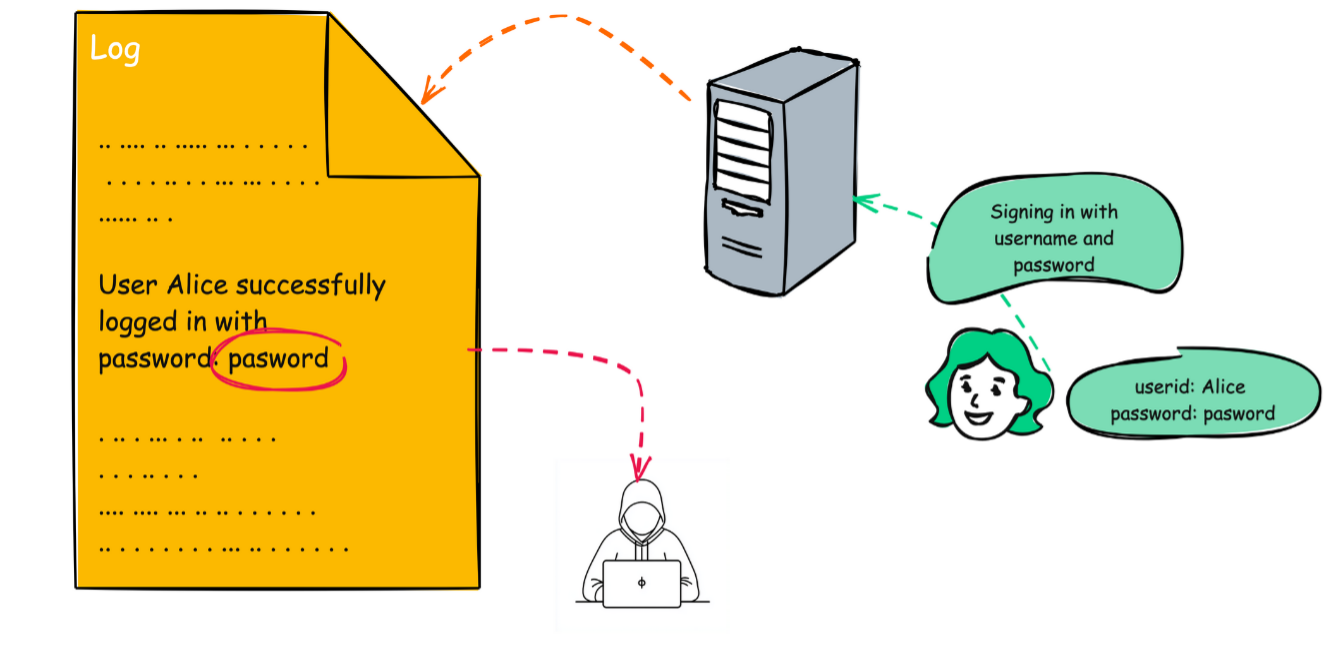
The product writes sensitive information to a log file.

Abstraction

Base

Structure

Simple

Likelihood of Exploit

Medium

Understand the problem

What is the problem?

The product writes sensitive information to a log file.

Root cause

How and when does the problem arise?

Lifecycle phase

Architecture and Design

COMMISSION: This weakness refers to an incorrect design related to an architectural security tactic.

Lifecycle phase

Implementation

Lifecycle phase

Operation

Risk

What does successful exploitation lead to?

Read Application Data

Affected security scopes: Confidentiality

Logging sensitive user data, full path names, or system information often provides attackers with an additional, less-protected path to acquiring the information.

Defence

How is it prevented and fixed?

Architecture and Design · Implementation

Defence to apply across several lifecycle phases

Detail
Consider seriously the sensitivity of the information written into log files. Do not write secrets into the log files.

Distribution

Distribution aşaması savunması

Detail
Remove debug log files before deploying the application into production.

Operation

Operational defence

Detail
Protect log files against unauthorized read/write.

Implementation

Implementation-phase defence

Detail
Adjust configurations appropriately when software is transitioned from a debug state to production.

Verification

How is it detected?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE diagram

Weakness relationships and flow
CWE-532 MITRE diagramı
CWE-532: Common Weakness Enumeration Entry CWE-532 · DayBreach Sözlük · DayBreach