CWE-787
Out-of-bounds Write
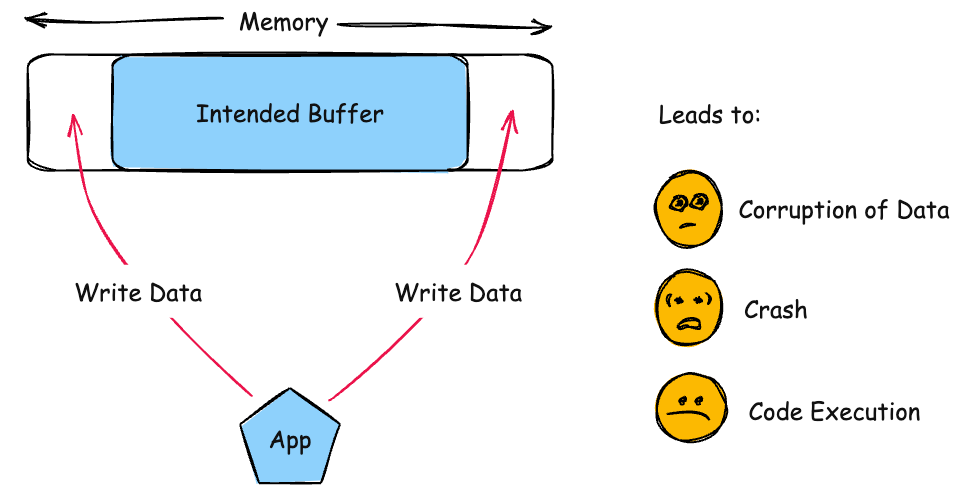
The product writes data past the end, or before the beginning, of the intended buffer.
Abstraction
Base
Structure
Simple
Likelihood of Exploit
High
Understand the problem
What is the problem?
Terminology
Alternate terms and usages
Memory Corruption
Root cause
How and when does the problem arise?
Lifecycle phase
Implementation
Risk
What does successful exploitation lead to?
Affected security scopes: Integrity
Affected security scopes: Availability
Affected security scopes: Other
Defence
How is it prevented and fixed?
Requirements
Language Selection
Detail
Requirements
Language Selection
Architecture and Design
Libraries or Frameworks
Detail
Architecture and Design
Libraries or Frameworks
This is not a complete solution, since many buffer overflows are not related to strings.
Operation · Build and Compilation
Environment Hardening
Detail
Operation · Build and Compilation
Environment Hardening
Effectiveness: Defense in Depth
This is not necessarily a complete solution, since these mechanisms only detect certain types of overflows. In addition, the result is still a denial of service, since the typical response is to exit the application.
Implementation
Implementation-phase defence
Detail
Implementation
Implementation-phase defence
Operation · Build and Compilation
Environment Hardening
Detail
Operation · Build and Compilation
Environment Hardening
Effectiveness: Defense in Depth
These techniques do not provide a complete solution. For instance, exploits frequently use a bug that discloses memory addresses in order to maximize reliability of code execution [REF-1337]. It has also been shown that a side-channel attack can bypass ASLR [REF-1333].
Operation
Environment Hardening
Detail
Operation
Environment Hardening
Effectiveness: Defense in Depth
This is not a complete solution, since buffer overflows could be used to overwrite nearby variables to modify the software's state in dangerous ways. In addition, it cannot be used in cases in which self-modifying code is required. Finally, an attack could still cause a denial of service, since the typical response is to exit the application.
Implementation
Implementation-phase defence
Detail
Implementation
Implementation-phase defence
Effectiveness: Moderate
This approach is still susceptible to calculation errors, including issues such as off-by-one errors (CWE-193) and incorrectly calculating buffer lengths (CWE-131).
Verification
How is it detected?
Automated Static Analysis
HighDetection techniques for buffer-related errors are more mature than for most other weakness types.
Automated Dynamic Analysis
Automated Dynamic Analysis
ModerateCrafted inputs are necessary to reach the code containing the error, such as generated by fuzzers. Also, these tools may reduce performance, and they only report the error condition - not the original mistake that led to the error.
MITRE diagram
Weakness relationships and flow