COMMON WEAKNESS ENUMERATIONIncomplete
CWE-863
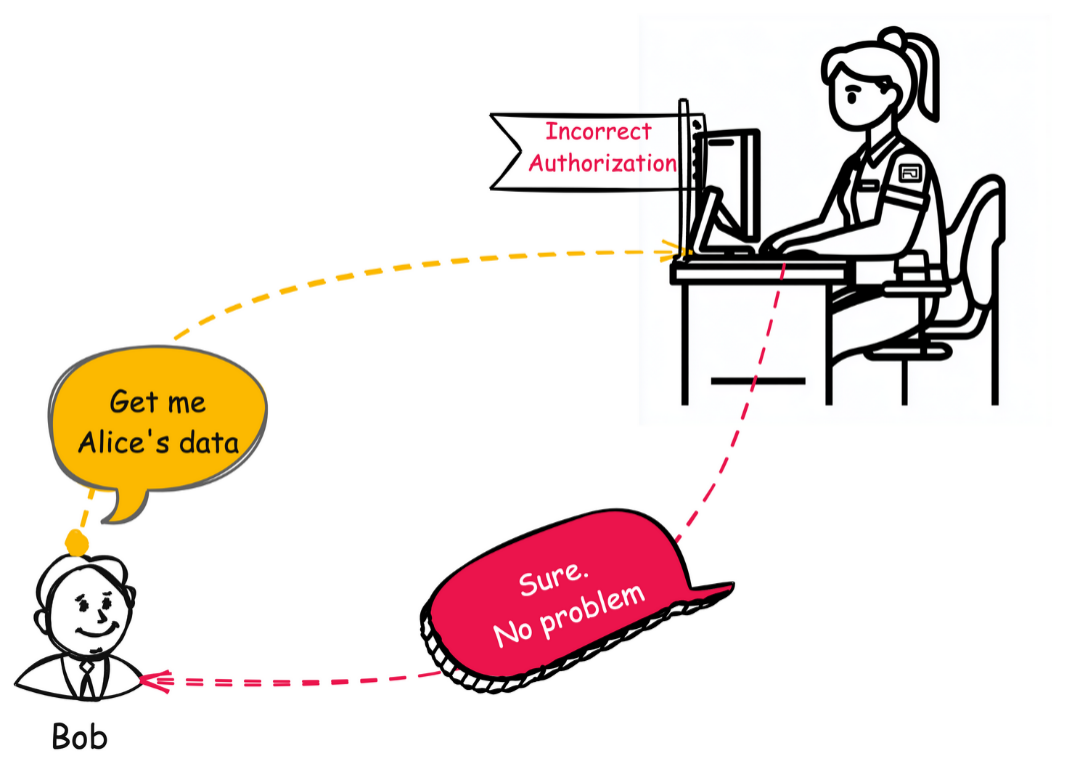
Incorrect Authorization
Abstraction
Class
Structure
Simple
Likelihood of Exploit
High
Understand the problem
What is the problem?
Terminology
Alternate terms and usages
AuthZ
Root cause
How and when does the problem arise?
Lifecycle phase
Architecture and Design
Lifecycle phase
Implementation
Lifecycle phase
Operation
Risk
What does successful exploitation lead to?
Read Application DataRead Files or Directories
Modify Application DataModify Files or Directories
Gain Privileges or Assume IdentityBypass Protection Mechanism
Execute Unauthorized Code or Commands
DoS: Crash, Exit, or RestartDoS: Resource Consumption (CPU)DoS: Resource Consumption (Memory)DoS: Resource Consumption (Other)
Defence
How is it prevented and fixed?
Architecture and Design
Architecture and design approach
Detail
Architecture and Design
Architecture and design approach
Architecture and Design
Architecture and design approach
Detail
Architecture and Design
Architecture and design approach
Architecture and Design
Libraries or Frameworks
Detail
Architecture and Design
Libraries or Frameworks
Architecture and Design
Architecture and design approach
Detail
Architecture and Design
Architecture and design approach
System Configuration · Installation
Defence to apply across several lifecycle phases
Detail
System Configuration · Installation
Defence to apply across several lifecycle phases
Verification
How is it detected?
Automated Static Analysis
LimitedAutomated Dynamic Analysis
Manual Analysis
ModerateManual Static Analysis - Binary or Bytecode
SOAR PartialDynamic Analysis with Automated Results Interpretation
SOAR PartialDynamic Analysis with Manual Results Interpretation
SOAR PartialManual Static Analysis - Source Code
SOAR PartialAutomated Static Analysis - Source Code
SOAR PartialArchitecture or Design Review
HighMITRE diagram
Weakness relationships and flow