COMMON WEAKNESS ENUMERATIONDraft

CWE-312

Cleartext Storage of Sensitive Information

The product stores sensitive information in cleartext within a resource that might be accessible to another control sphere.

Soyutlama

Base

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The product stores sensitive information in cleartext within a resource that might be accessible to another control sphere.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Architecture and Design

OMISSION: This weakness is caused by missing a security tactic during the architecture and design phase.

Risk

Başarılı sömürü neye yol açar?

Read Application Data

Etkilenen güvenlik alanları: Confidentiality

An attacker with access to the system could read sensitive information stored in cleartext (i.e., unencrypted). Even if the information is encoded in a way that is not human-readable, certain techniques could determine which encoding is being used, then decode the information.

Savunma

Nasıl önlenir ve çözülür?

Implementation · System Configuration · Operation

Birden fazla yaşam döngüsü evresinde uygulanacak savunma

Detay
When storing data in the cloud (e.g., S3 buckets, Azure blobs, Google Cloud Storage, etc.), use the provider's controls to encrypt the data at rest. [REF-1297] [REF-1299] [REF-1301]

Implementation · System Configuration · Operation

Birden fazla yaşam döngüsü evresinde uygulanacak savunma

Detay
In some systems/environments such as cloud, the use of "double encryption" (at both the software and hardware layer) might be required, and the developer might be solely responsible for both layers, instead of shared responsibility with the administrator of the broader system/environment.

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
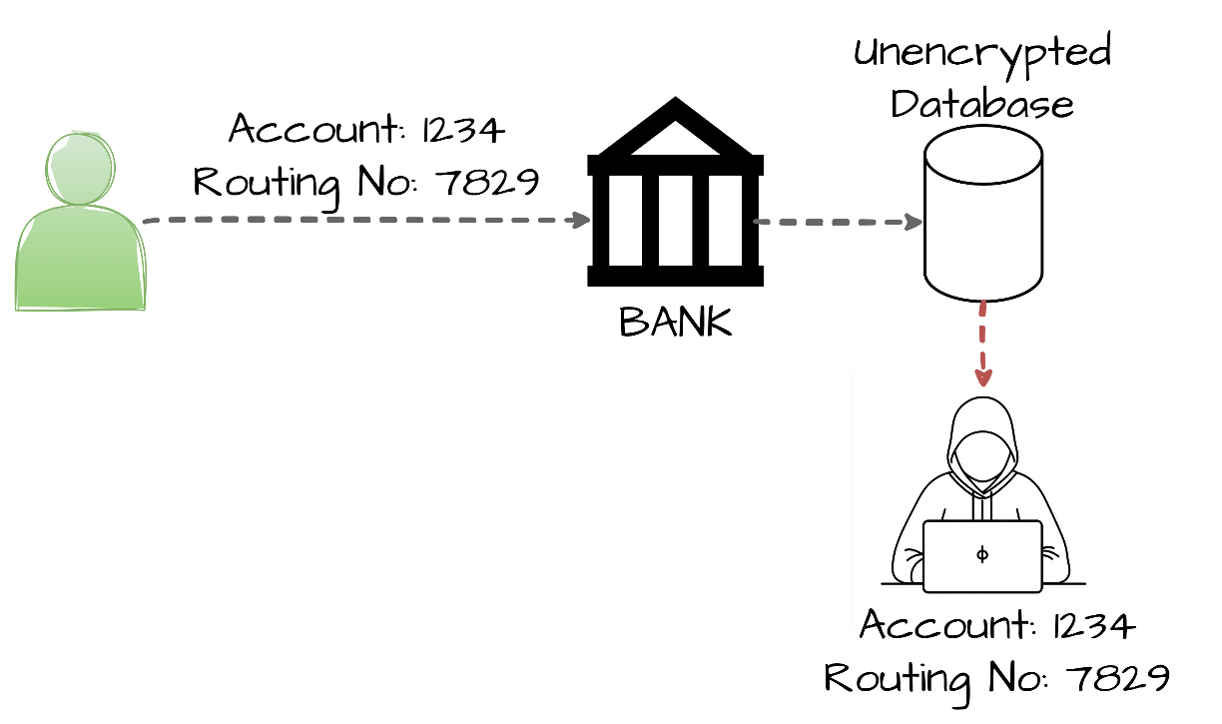
CWE-312 MITRE diagramı
CWE-312: Common Weakness Enumeration Entry CWE-312 · DayBreach Sözlük · DayBreach