COMMON WEAKNESS ENUMERATIONIncomplete
CWE-425
Direct Request ('Forced Browsing')
Soyutlama
Base
Yapı
Simple
Sömürü İhtimali
Medium
Problemi anla
Problem nedir?
Terminoloji
Alternatif adlar ve kullanım biçimleri
forced browsing
Kök neden
Problem nasıl ve ne zaman oluşur?
Yaşam döngüsü evresi
Implementation
Yaşam döngüsü evresi
Operation
Risk
Başarılı sömürü neye yol açar?
Read Application DataModify Application DataExecute Unauthorized Code or CommandsGain Privileges or Assume Identity
Savunma
Nasıl önlenir ve çözülür?
Architecture and Design · Operation
Birden fazla yaşam döngüsü evresinde uygulanacak savunma
Detay
Architecture and Design · Operation
Birden fazla yaşam döngüsü evresinde uygulanacak savunma
Architecture and Design
Mimari ve tasarım yaklaşımı
Detay
Architecture and Design
Mimari ve tasarım yaklaşımı
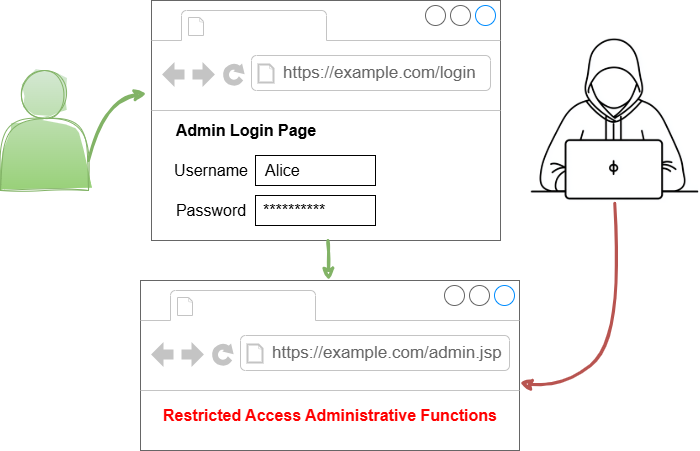
MITRE görseli
Zafiyet ilişkisi ve akışı