COMMON WEAKNESS ENUMERATIONDraft

CWE-598

Use of HTTP Request With Sensitive Query String

The web application uses an HTTP method to process a request, but the request includes sensitive information in the query string.

Soyutlama

Variant

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The web application uses an HTTP method to process a request, but the request includes sensitive information in the query string.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Architecture and Design

Yaşam döngüsü evresi

Implementation

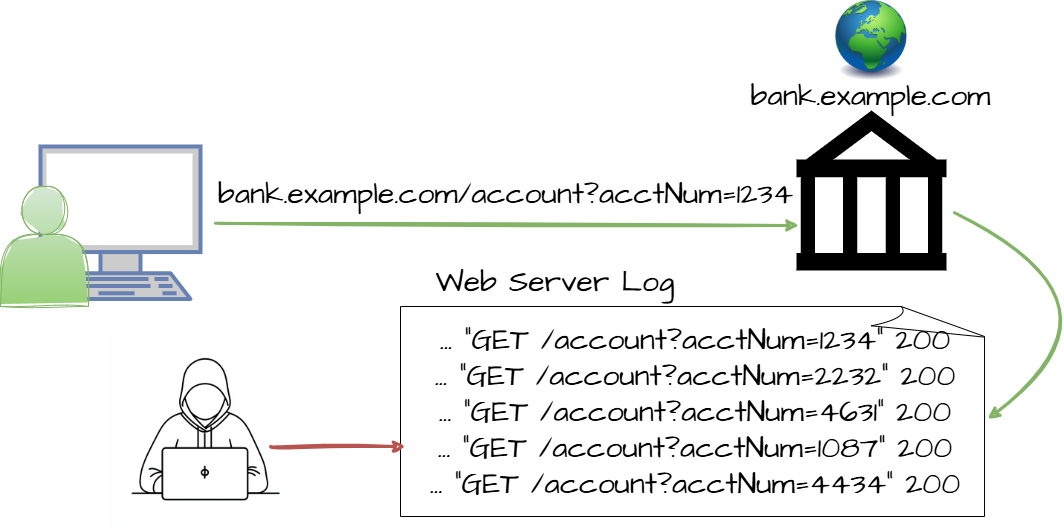
While a query string is frequently used for GET methods, sometimes it is included with other methods such as POST, DELETE, and PUT. The query string for the URL could be saved in the browser's history, passed through Referers to other web sites, stored in web logs, or otherwise recorded in other sources.

Risk

Başarılı sömürü neye yol açar?

Read Application Data

Etkilenen güvenlik alanları: Confidentiality

At a minimum, attackers can garner information from query strings that can be utilized in escalating their method of attack, such as information about the internal workings of the application or database column names. Successful exploitation of query string parameter vulnerabilities could lead to an attacker impersonating a legitimate user, obtaining proprietary data, or simply executing actions not intended by the application developers. Examples of sensitive information may include secrets such as session identifiers, passwords, access tokens, or API keys; Personally Identifiable Information (PII) such as email addresses or phone numbers; records or logs of private activities; communications that are expected to be private; etc. Successful exploitation of query string parameter vulnerabilities could lead to an attacker impersonating a legitimate user, obtaining proprietary data, or simply executing actions not intended by the application developers.

Savunma

Nasıl önlenir ve çözülür?

Implementation

Uygulama aşaması savunması

Detay
When sending sensitive information, only include it in the request body or request headers instead of the query string. This may require avoiding use of GET requests.

Doğrulama

Nasıl tespit edilir?

Automated Static Analysis

High
Automated static analysis, commonly referred to as Static Application Security Testing (SAST), can find some instances of this weakness by analyzing source code (or binary/compiled code) without having to execute it. Typically, this is done by building a model of data flow and control flow, then searching for potentially-vulnerable patterns that connect "sources" (origins of input) with "sinks" (destinations where the data interacts with external components, a lower layer such as the OS, etc.)

MITRE görseli

Zafiyet ilişkisi ve akışı
CWE-598 MITRE diagramı
CWE-598: Common Weakness Enumeration Entry CWE-598 · DayBreach Sözlük · DayBreach