COMMON WEAKNESS ENUMERATIONIncomplete

CWE-599

Missing Validation of OpenSSL Certificate

The product uses OpenSSL and trusts or uses a certificate without using the SSL_get_verify_result() function to ensure that the certificate satisfies all necessary security requirements.

Soyutlama

Variant

Yapı

Simple

Sömürü İhtimali

Medium

Problemi anla

Problem nedir?

The product uses OpenSSL and trusts or uses a certificate without using the SSL_get_verify_result() function to ensure that the certificate satisfies all necessary security requirements.

Kök neden

Problem nasıl ve ne zaman oluşur?

Yaşam döngüsü evresi

Implementation

Risk

Başarılı sömürü neye yol açar?

Read Application Data

Etkilenen güvenlik alanları: Confidentiality

The data read may not be properly secured - it might be viewed by an attacker.
Bypass Protection MechanismGain Privileges or Assume Identity

Etkilenen güvenlik alanları: Access Control

Trust afforded to the system in question may allow for spoofing or redirection attacks.
Gain Privileges or Assume Identity

Etkilenen güvenlik alanları: Access Control

If the certificate is not checked, it may be possible for a redirection or spoofing attack to allow a malicious host with a valid certificate to provide data under the guise of a trusted host. While the attacker in question may have a valid certificate, it may simply be a valid certificate for a different site. This could allow an attacker to use an invalid certificate to claim to be a trusted host, use expired certificates, or conduct other attacks that could be detected if the certificate is properly validated. In order to ensure data integrity, we must check that the certificate is valid, and that it pertains to the site we wish to access.

Savunma

Nasıl önlenir ve çözülür?

Architecture and Design

Mimari ve tasarım yaklaşımı

Detay
Ensure that proper authentication is included in the system design.

Implementation

Uygulama aşaması savunması

Detay
Understand and properly implement all checks necessary to ensure the identity of entities involved in encrypted communications.

MITRE görseli

Zafiyet ilişkisi ve akışı
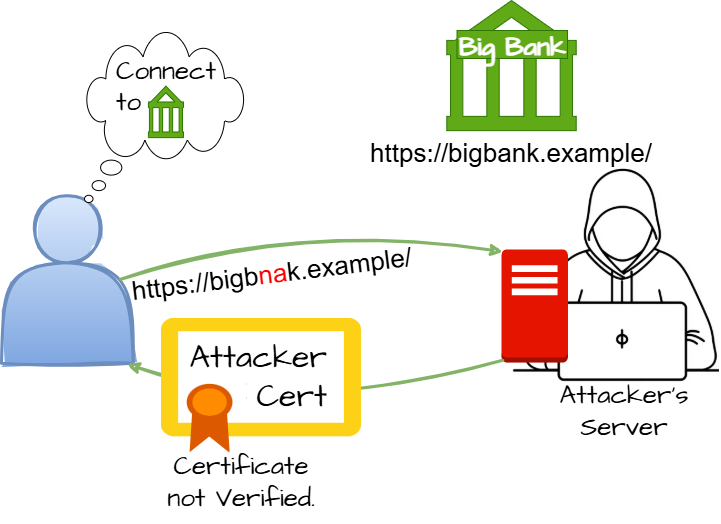
CWE-599 MITRE diagramı
CWE-599: Common Weakness Enumeration Entry CWE-599 · DayBreach Sözlük · DayBreach