CWE-120
Buffer Copy without Checking Size of Input ('Classic Buffer Overflow')
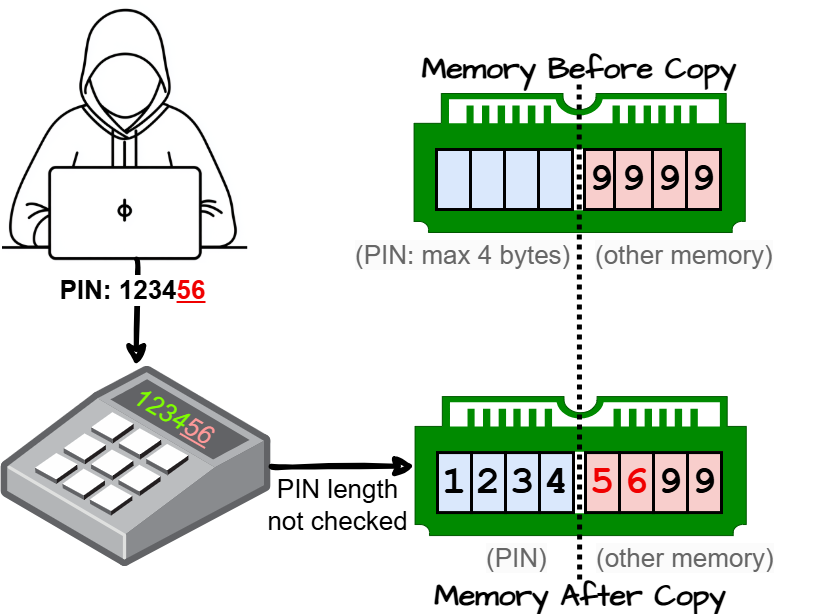
The product copies an input buffer to an output buffer without verifying that the size of the input buffer is less than the size of the output buffer.
Abstraction
Base
Structure
Simple
Likelihood of Exploit
High
Understand the problem
What is the problem?
Terminology
Alternate terms and usages
Classic Buffer Overflow
Unbounded Transfer
Root cause
How and when does the problem arise?
Lifecycle phase
Implementation
Risk
What does successful exploitation lead to?
Affected security scopes: Integrity, Confidentiality, Availability
Affected security scopes: Availability
Defence
How is it prevented and fixed?
Requirements
Language Selection
Detail
Requirements
Language Selection
Architecture and Design
Libraries or Frameworks
Detail
Architecture and Design
Libraries or Frameworks
This is not a complete solution, since many buffer overflows are not related to strings.
Operation · Build and Compilation
Environment Hardening
Detail
Operation · Build and Compilation
Environment Hardening
Effectiveness: Defense in Depth
This is not necessarily a complete solution, since these mechanisms only detect certain types of overflows. In addition, the result is still a denial of service, since the typical response is to exit the application.
Implementation
Implementation-phase defence
Detail
Implementation
Implementation-phase defence
Implementation
Input Validation
Detail
Implementation
Input Validation
Architecture and Design
Architecture and design approach
Detail
Architecture and Design
Architecture and design approach
Operation · Build and Compilation
Environment Hardening
Detail
Operation · Build and Compilation
Environment Hardening
Effectiveness: Defense in Depth
These techniques do not provide a complete solution. For instance, exploits frequently use a bug that discloses memory addresses in order to maximize reliability of code execution [REF-1337]. It has also been shown that a side-channel attack can bypass ASLR [REF-1333].
Operation
Environment Hardening
Detail
Operation
Environment Hardening
Effectiveness: Defense in Depth
This is not a complete solution, since buffer overflows could be used to overwrite nearby variables to modify the software's state in dangerous ways. In addition, it cannot be used in cases in which self-modifying code is required. Finally, an attack could still cause a denial of service, since the typical response is to exit the application.
Build and Compilation · Operation
Defence to apply across several lifecycle phases
Detail
Build and Compilation · Operation
Defence to apply across several lifecycle phases
Implementation
Implementation-phase defence
Detail
Implementation
Implementation-phase defence
Effectiveness: Moderate
This approach is still susceptible to calculation errors, including issues such as off-by-one errors (CWE-193) and incorrectly calculating buffer lengths (CWE-131).
Architecture and Design
Enforcement by Conversion
Detail
Architecture and Design
Enforcement by Conversion
Architecture and Design · Operation
Environment Hardening
Detail
Architecture and Design · Operation
Environment Hardening
Architecture and Design · Operation
Sandbox or Jail
Detail
Architecture and Design · Operation
Sandbox or Jail
Effectiveness: Limited
The effectiveness of this mitigation depends on the prevention capabilities of the specific sandbox or jail being used and might only help to reduce the scope of an attack, such as restricting the attacker to certain system calls or limiting the portion of the file system that can be accessed.
Verification
How is it detected?
Automated Static Analysis
HighDetection techniques for buffer-related errors are more mature than for most other weakness types.
Automated Dynamic Analysis
Manual Analysis
Automated Dynamic Analysis
ModerateCrafted inputs are necessary to reach the code containing the error, such as generated by fuzzers. Also, these tools may reduce performance, and they only report the error condition - not the original mistake that led to the error.
Automated Static Analysis - Binary or Bytecode
HighManual Static Analysis - Binary or Bytecode
SOAR PartialDynamic Analysis with Automated Results Interpretation
SOAR PartialDynamic Analysis with Manual Results Interpretation
SOAR PartialManual Static Analysis - Source Code
SOAR PartialAutomated Static Analysis - Source Code
HighArchitecture or Design Review
HighMITRE diagram
Weakness relationships and flow